From Data Maturity Assessment to Governance That Runs in Your Systems
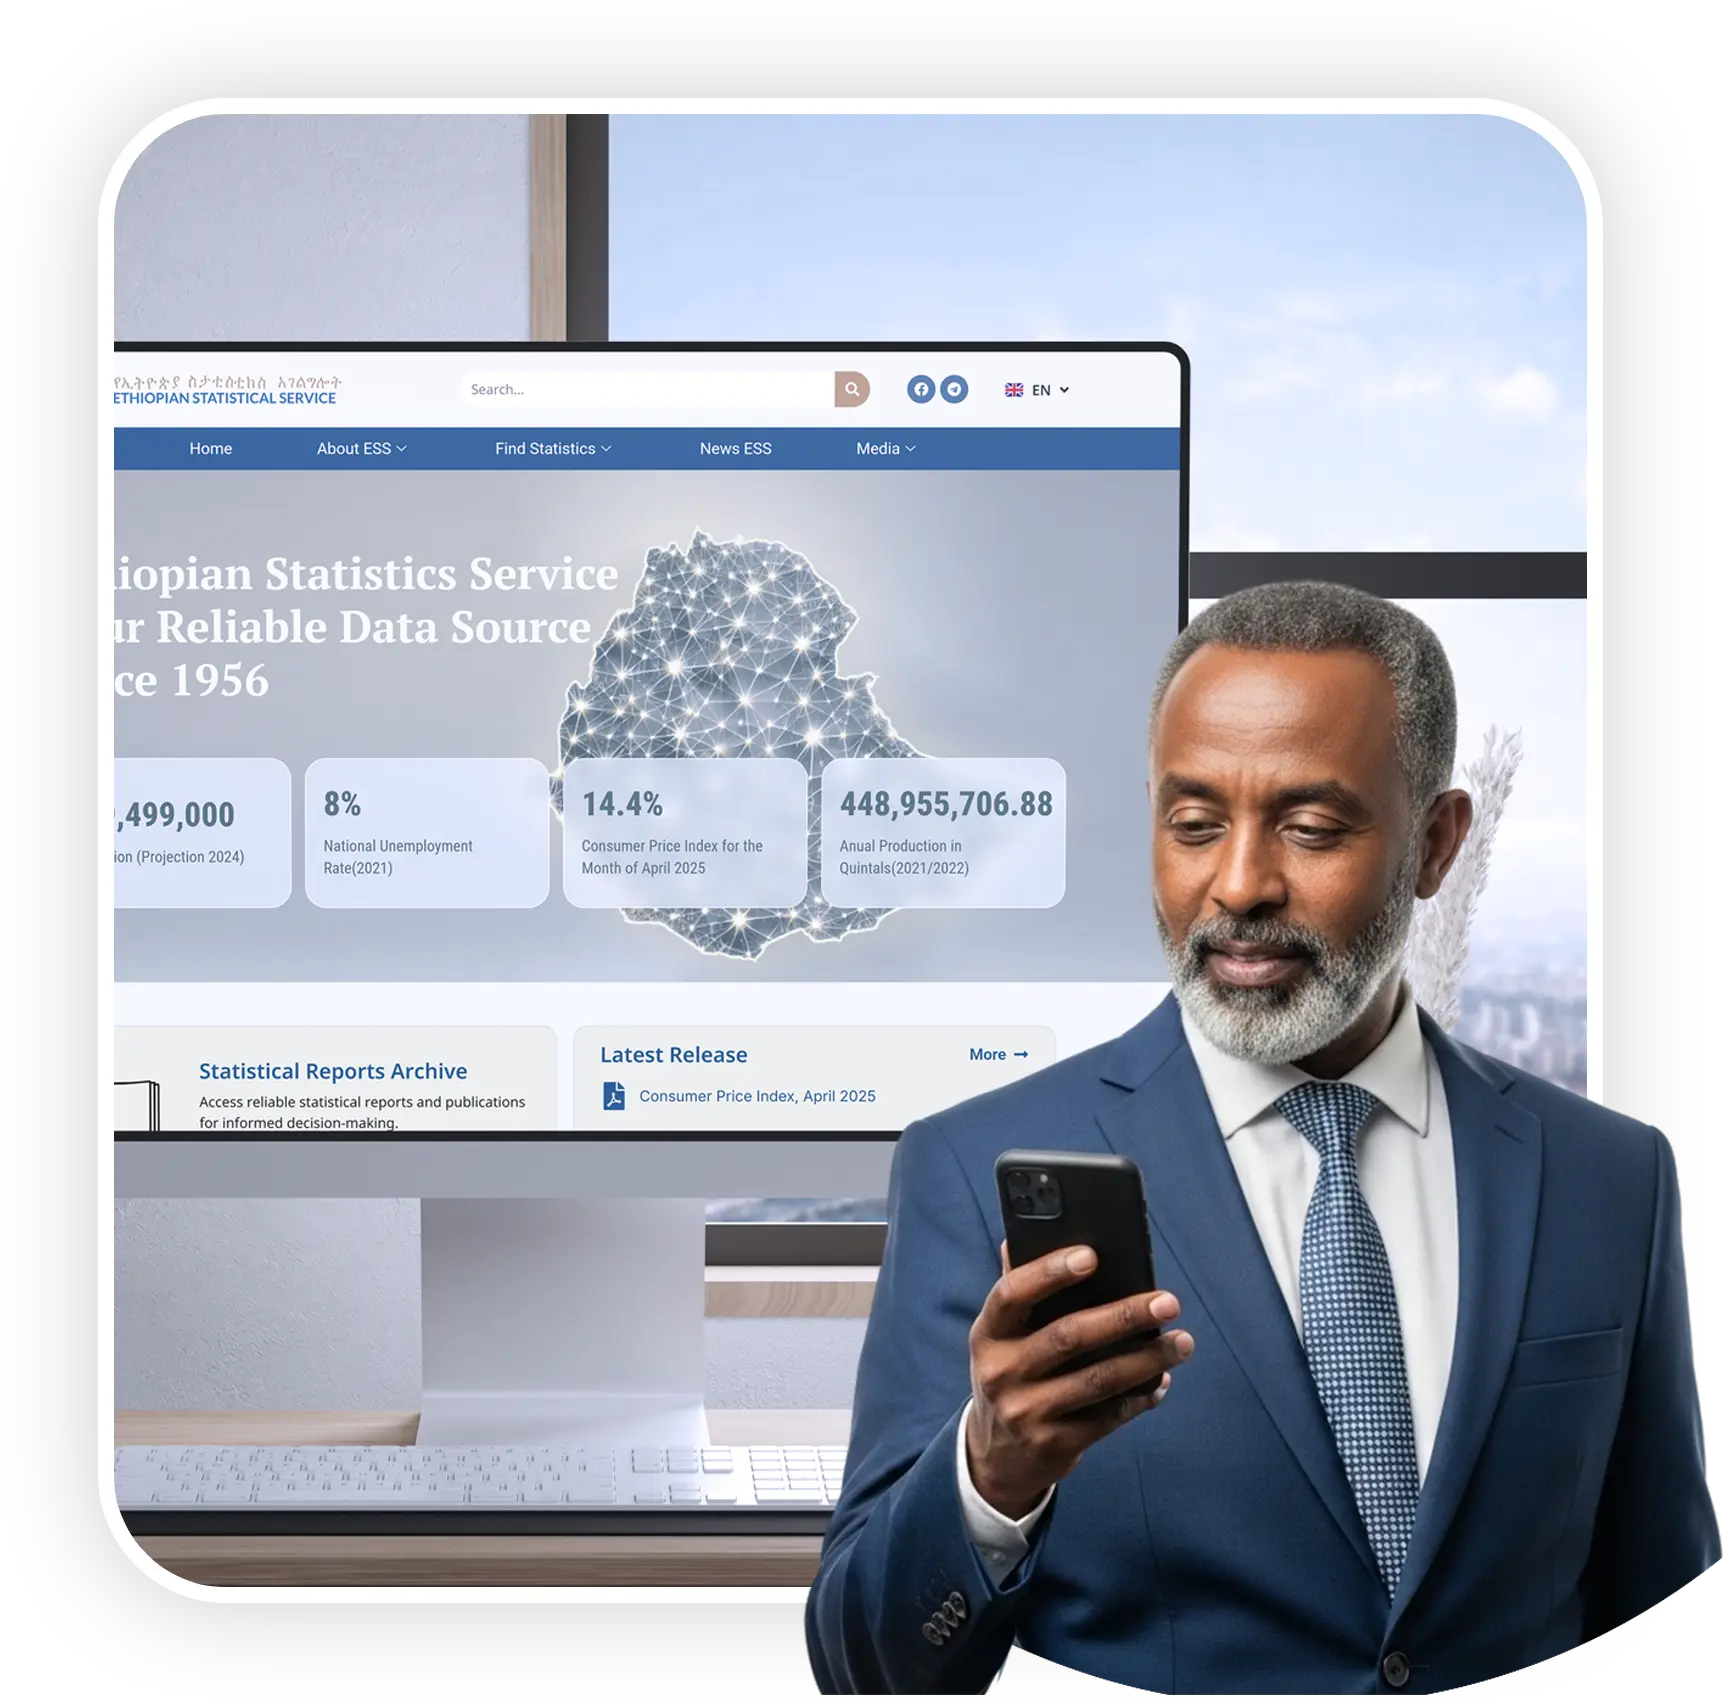
360Ground helps Ethiopian banks, regulators, ministries and enterprises assess data maturity, set a data strategy and implement data governance. We score people, process, technology, data quality, security and privacy, then deliver a roadmap, a governance framework with clear ownership, policies, a data dictionary and quality rules, and readiness for the Personal Data Protection Proclamation No. 1321/2024. We then build the controls into your systems: catalogues, validation, access control and audit trails. We have done this at national scale, with governed platforms for ESS, INSA and the Ministry of Innovation and Technology, and we partner with IRIS Business Services on regulatory data.
A scored assessment of your data people, processes, technology, quality, security and privacy against a recognised framework, giving a clear baseline and a prioritised roadmap.
Data Strategy & Roadmap
A data strategy tied to your business, policy and regulatory goals, with priorities, phased investment and measurable targets your leadership can approve and track.
Data Governance Framework
Data owners and stewards, a governance council, decision rights and an operating model, so every dataset has someone accountable for its quality and use.
Personal Data Protection Readiness
Data inventory, records of processing, impact assessments, consent, retention and breach procedures aligned to Proclamation No. 1321/2024 and registration with the Ethiopian Communications Authority.
Data Policies, Quality & Master Data
Classification, management, sharing and retention policies, plus data quality rules, a data dictionary and master data management for customers, products and locations.
Regulatory Data & Governance Tooling
Regulatory reporting data quality for banks with our partner IRIS, plus the catalogues, validation rules and immutable audit logs that make governance work daily.
Case Studies
Every project is a journey, and we measure success by the results our clients achieve. From MVPs that disrupt industries to enterprise solutions that scale globally, these stories show how we transform ideas into market-leading solutions.
A data maturity assessment measures how well your organisation manages and uses data today, and what to fix first. It scores areas such as governance and ownership, data quality, architecture and integration, security and privacy, analytics and skills against a recognised framework such as DAMA-DMBOK. You receive a scorecard showing where you stand, the gaps that carry the most risk and a prioritised roadmap. Ministries and banks use it as the baseline for a data strategy.
Does the Personal Data Protection Proclamation apply to our bank?
Yes. Proclamation No. 1321/2024, in force since July 2024, applies to organisations in Ethiopia that collect or process personal data, and banks hold large volumes of customer data. Key duties include a lawful basis for processing, data subject rights, security safeguards, impact assessments for high-risk processing, rules on transfers abroad and notifying the authority of a breach within 72 hours. We provide technical compliance; take legal advice on how the law applies to you.
How do we register as a data controller with the ECA?
The Ethiopian Communications Authority supervises Proclamation No. 1321/2024, and controllers and processors are expected to register with it before processing personal data. Registration asks what personal data you hold, why, who receives it and how it is protected, so the real work is a complete data inventory and record of processing. We build that inventory and the supporting documents. Confirm the current procedure, forms and deadlines directly with the ECA.
What should a data governance framework include?
At minimum: clear roles, including data owners, stewards and a governance council; policies for data management, classification, sharing and retention; a data dictionary and metadata standards; data quality rules with measures and thresholds; access control and audit trails; and a process for issues and change. It should also map to your legal duties, such as Proclamation No. 1321/2024 and sector rules. A framework only works when these controls are built into your systems.
How long does a data maturity assessment take?
A focused assessment of one organisation typically takes a few weeks, depending on the number of departments, systems and datasets in scope and how quickly staff are available for interviews. It runs in four steps: scoping, interviews and system review, scoring, and a roadmap presented to leadership. Multi-agency or national programmes take longer and are usually phased. Tell us your scope, and we will confirm the duration, deliverables and price in birr.
What is the difference between data governance and data management?
Data governance sets the rules: who owns each dataset, who may access or change it, which quality standards apply and how compliance is proven. Data management does the work that follows those rules: collecting, storing, integrating, cleaning, securing and delivering data every day. Governance without management stays on paper, and management without governance produces inconsistent numbers. 360Ground covers both, from the framework to the systems that enforce it.